Product Security Policy
Commitment to Product Security
NACHI-FUJIKOSHI CORP. (hereinafter referred to as the “Company”) regards product cybersecurity as one of the essential elements of product quality.
In recent years, cybersecurity threats affecting the manufacturing industry have become increasingly sophisticated and diverse. Products with network connectivity are therefore also required to incorporate appropriate security measures from the design and development stages.
To provide customers with safe and reliable products and services, the Company promotes security activities throughout the entire product life cycle, from planning, design and development through operation and disposal, taking into account the requirements and principles of applicable laws and regulations in each country, including the European Union Cyber Resilience Act (CRA), as well as the international standard IEC 62443.
Basic Policy
- Security by Design
The Company endeavors to incorporate security considerations into product planning, design, development and evaluation process and to continuously strengthen such practices. - Risk-Based Security Measures
The Company aims to perform threat analyses and risk assessments for its products and to implement appropriate security measures based on the results. - Vulnerability Management
The Company endeavors to collect and monitor vulnerability information concerning its products and to evaluate and address such information as appropriate. - Supply Chain Security
The Company is committed to promoting security throughout its supply chain, including software components and third-party libraries. - Continuous Improvement
The Company is committed to continuously improving its product security activities in light of applicable laws and regulations, industry standards and emerging cybersecurity threats.
Product Security Governance Structure
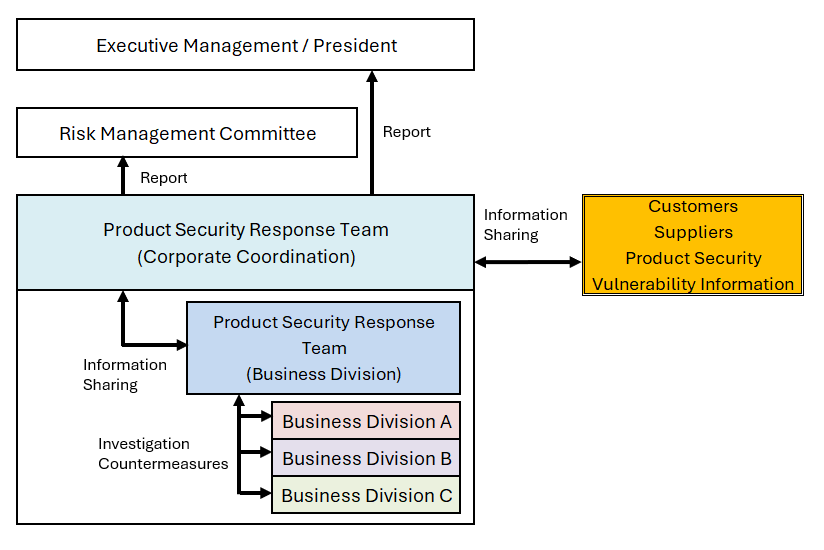
The Company is establishing and continuously enhancing an organizational framework for product security in order to respond appropriately to product vulnerabilities and improve security quality.
Relevant departments work in coordination to address product security issues and promote vulnerability management activities in a prompt and appropriate manner.
- Product Security Response Team
Policy for Receiving and Disclosing Vulnerability Information
Reporting Vulnerabilities
When contacting us, please provide the following information to the extent possible:
- Country of Use
- Name and model number of the affected product
- Description of the vulnerability
- Steps to reproduce the vulnerability
- Potential impact
- Test results or reference materials
Our Response
The Company will review the information received and may request additional information as necessary.
If a vulnerability is confirmed, the Company will assess its severity and take appropriate measures, such as providing corrected software or workarounds, or informing users of security information.
Disclosure of Information
If the Company determines that disclosure is necessary after carefully considering the potential impact on customers and society, it will inform the impacted users (or where appropriate, all users) of vulnerability information and mitigation information through appropriate channels.
To protect users, please refrain from publicly disclosing vulnerability information before the Company has completed preparations for the relevant mitigation measures.
Disclaimer
The Company will endeavor to respond in good faith to vulnerability information provided to us. However, depending on the content of the information and the circumstances, the Company may not be able to provide an individual response.
The Company welcomes the provision of vulnerability information that contributes to improving product security. When providing such information, please do not conduct investigations or testing through unauthorized access or by any other method that violates applicable laws and regulations.